Who is associated?
Separate the database account from the application user. Missing attribution deserves investigation; it does not identify an attacker.
NANORI / RESOURCES
Understand the investigation, examine the capabilities, and define what a useful evaluation should prove.
Explore the documents ↓AN INVESTIGATION QUESTION
A shared account and a familiar SELECT can conceal a change in how much data is being read. Examine the whole window, the available identity and the data involved before deciding what the activity means.
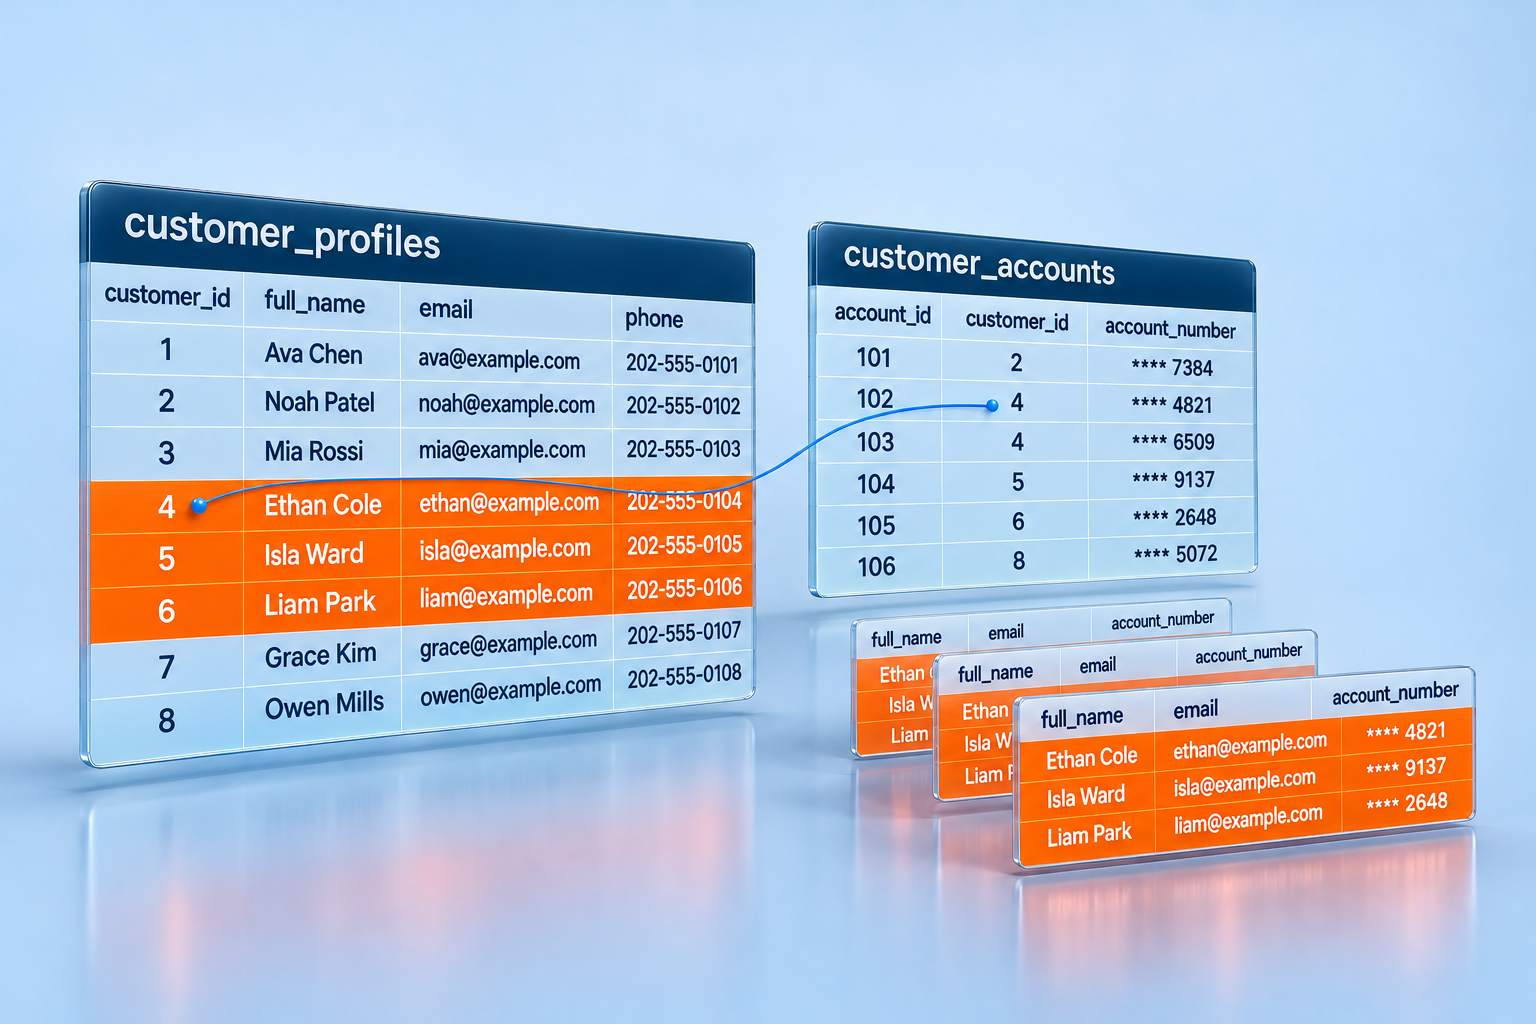
01Customer profilesNames and contact information
02Linked accountsPersonal data connected to financial records
03Query resultsSelected information copied through reads
Separate the database account from the application user. Missing attribution deserves investigation; it does not identify an attacker.
Compare extraction, sources, tools and data access with the available baseline. Check whether the profile is still learning.
Review the scoped statements and the business context. An expected report and an unauthorized extraction may begin with similar SQL.
SOLUTION BRIEF / ENGLISH
Explore application-user attribution with Trace and investigation in Oversight. Follow shared-account activity into the identity context, risk findings and evidence available for review.
DATA SHEET / ENGLISH
A technical evaluation reference covering capture, attribution, risk detection, evidence retention and integration. Understand both the available capabilities and the conditions they depend on.
MAKE THE EVALUATION COUNT
Attribution: two application users sharing one database account, with their captured identities kept distinct.
Capture: visible statements and encryption metadata checked separately on your intended connection path.
Investigation: a finding linked to statements, an explicit review outcome and an export with the applicable retention policy.
Sign in for product guides, deployment architectures, integration references, and the resources available to your customer or partner account.
Sign in to the library ↗COMMON QUESTIONS
Lens and Oversight are deployed together for database monitoring and investigation. Trace is optional when you need application-user attribution, and can also be used independently with another compatible monitoring product.
Application-user attribution depends on available application context. A shared database account alone does not identify the person behind it, and missing context remains unknown.
No. Encryption state and statement visibility are different questions. Coverage depends on the engine, connection path, and configuration. Review the actual environment before deployment.
Sammy proposes searches and policy changes for review. Your analysts decide when to run a search or save a policy change.
Product documentation, detailed deployment architectures, and integration guidance belong in the authenticated customer and partner library. Public briefs and data sheets are available without signing in.