See the activity in context.
Explore captured statements, database accounts, available application-user context, and the relationships between users, applications, and tables.
NANORI OVERSIGHT / MONITORING & INVESTIGATION
Follow database activity from the captured statement to the identity context, behavior, and evidence behind it.
Request a demo ↗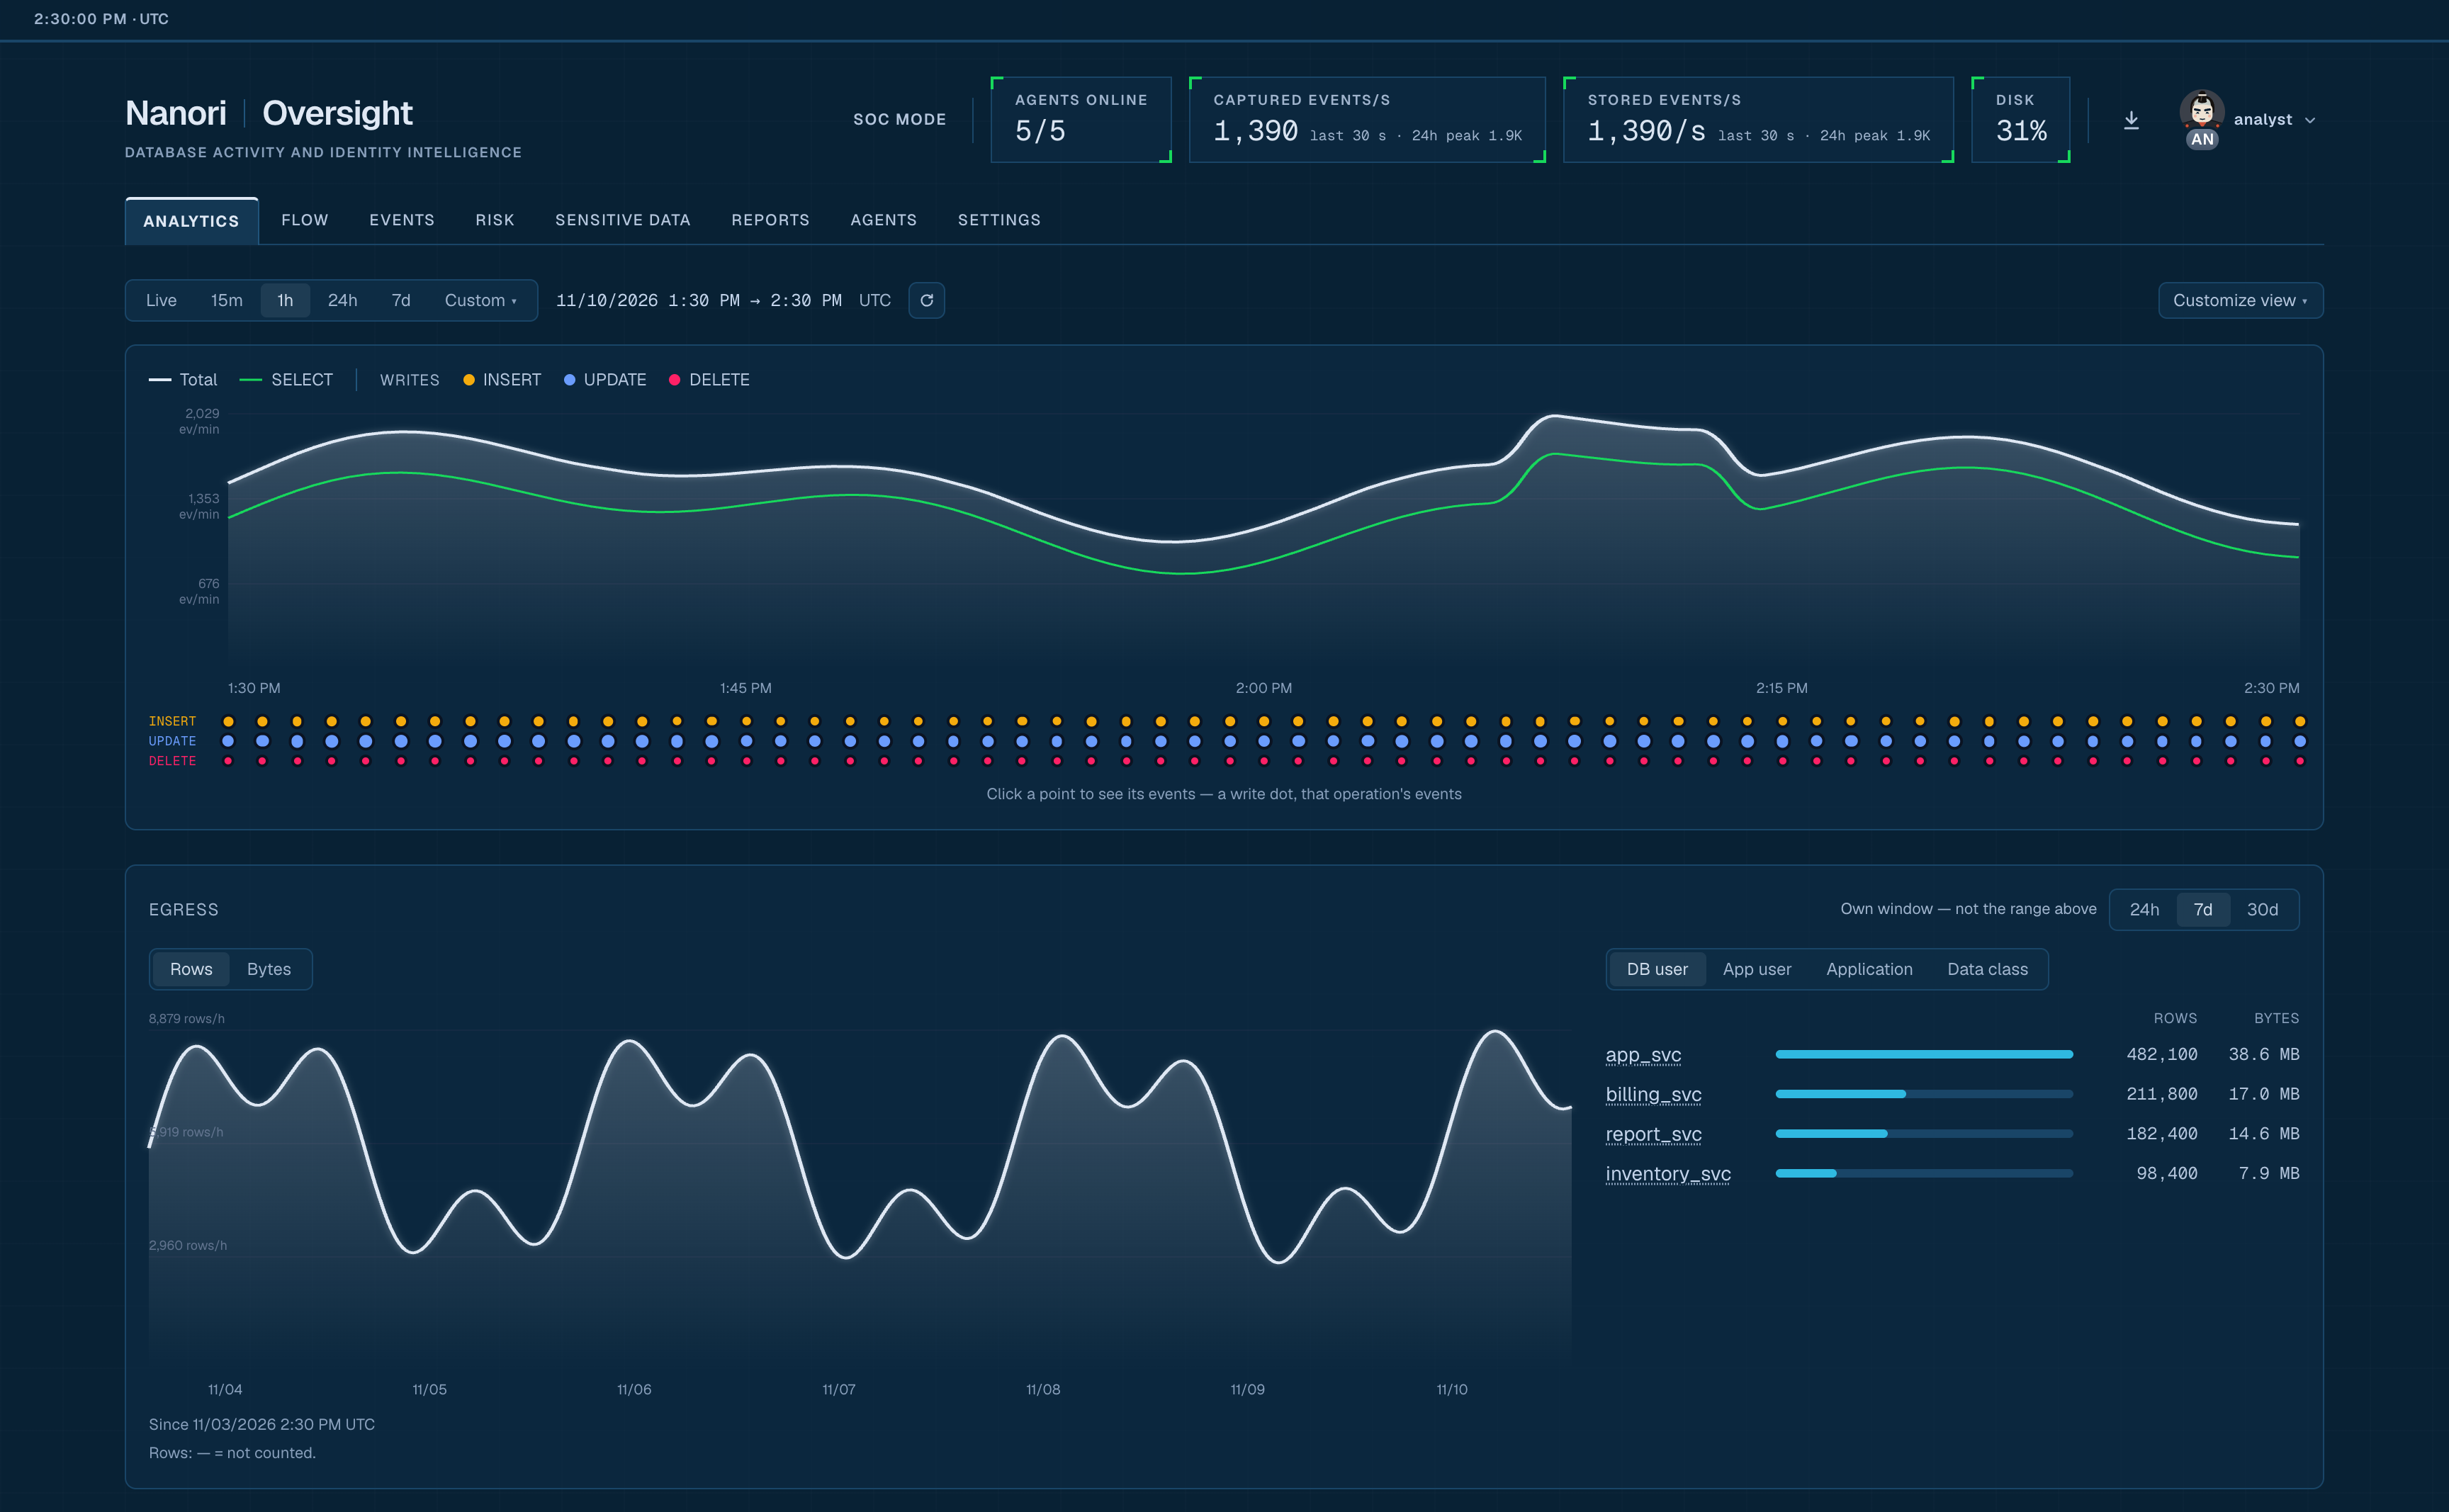
Explore captured statements, database accounts, available application-user context, and the relationships between users, applications, and tables.
Examine behavioral risk findings, extraction patterns, unusual identity behavior, and sensitive-data access. Compare observed activity with the available history before deciding what happened.
Inspect related statements, group alerts into incidents, apply audit policies, and export Events results as CSV or Parquet.
Nanori Oversight and Nanori Lens are deployed together. Add Nanori Trace when you need application-user attribution.
Findings support investigation. Baseline-based analysis requires sufficient observed history; available context depends on the captured activity.
Read the solution brief ↗