Carry the context the application knows.
Trace adds available application-user context to SQL statements so compatible monitoring tools can relate database activity to the application request.
NANORI TRACE / APPLICATION-USER ATTRIBUTION
Bring the application user into the database investigation, even when many people share the same database account.
Request a demo ↗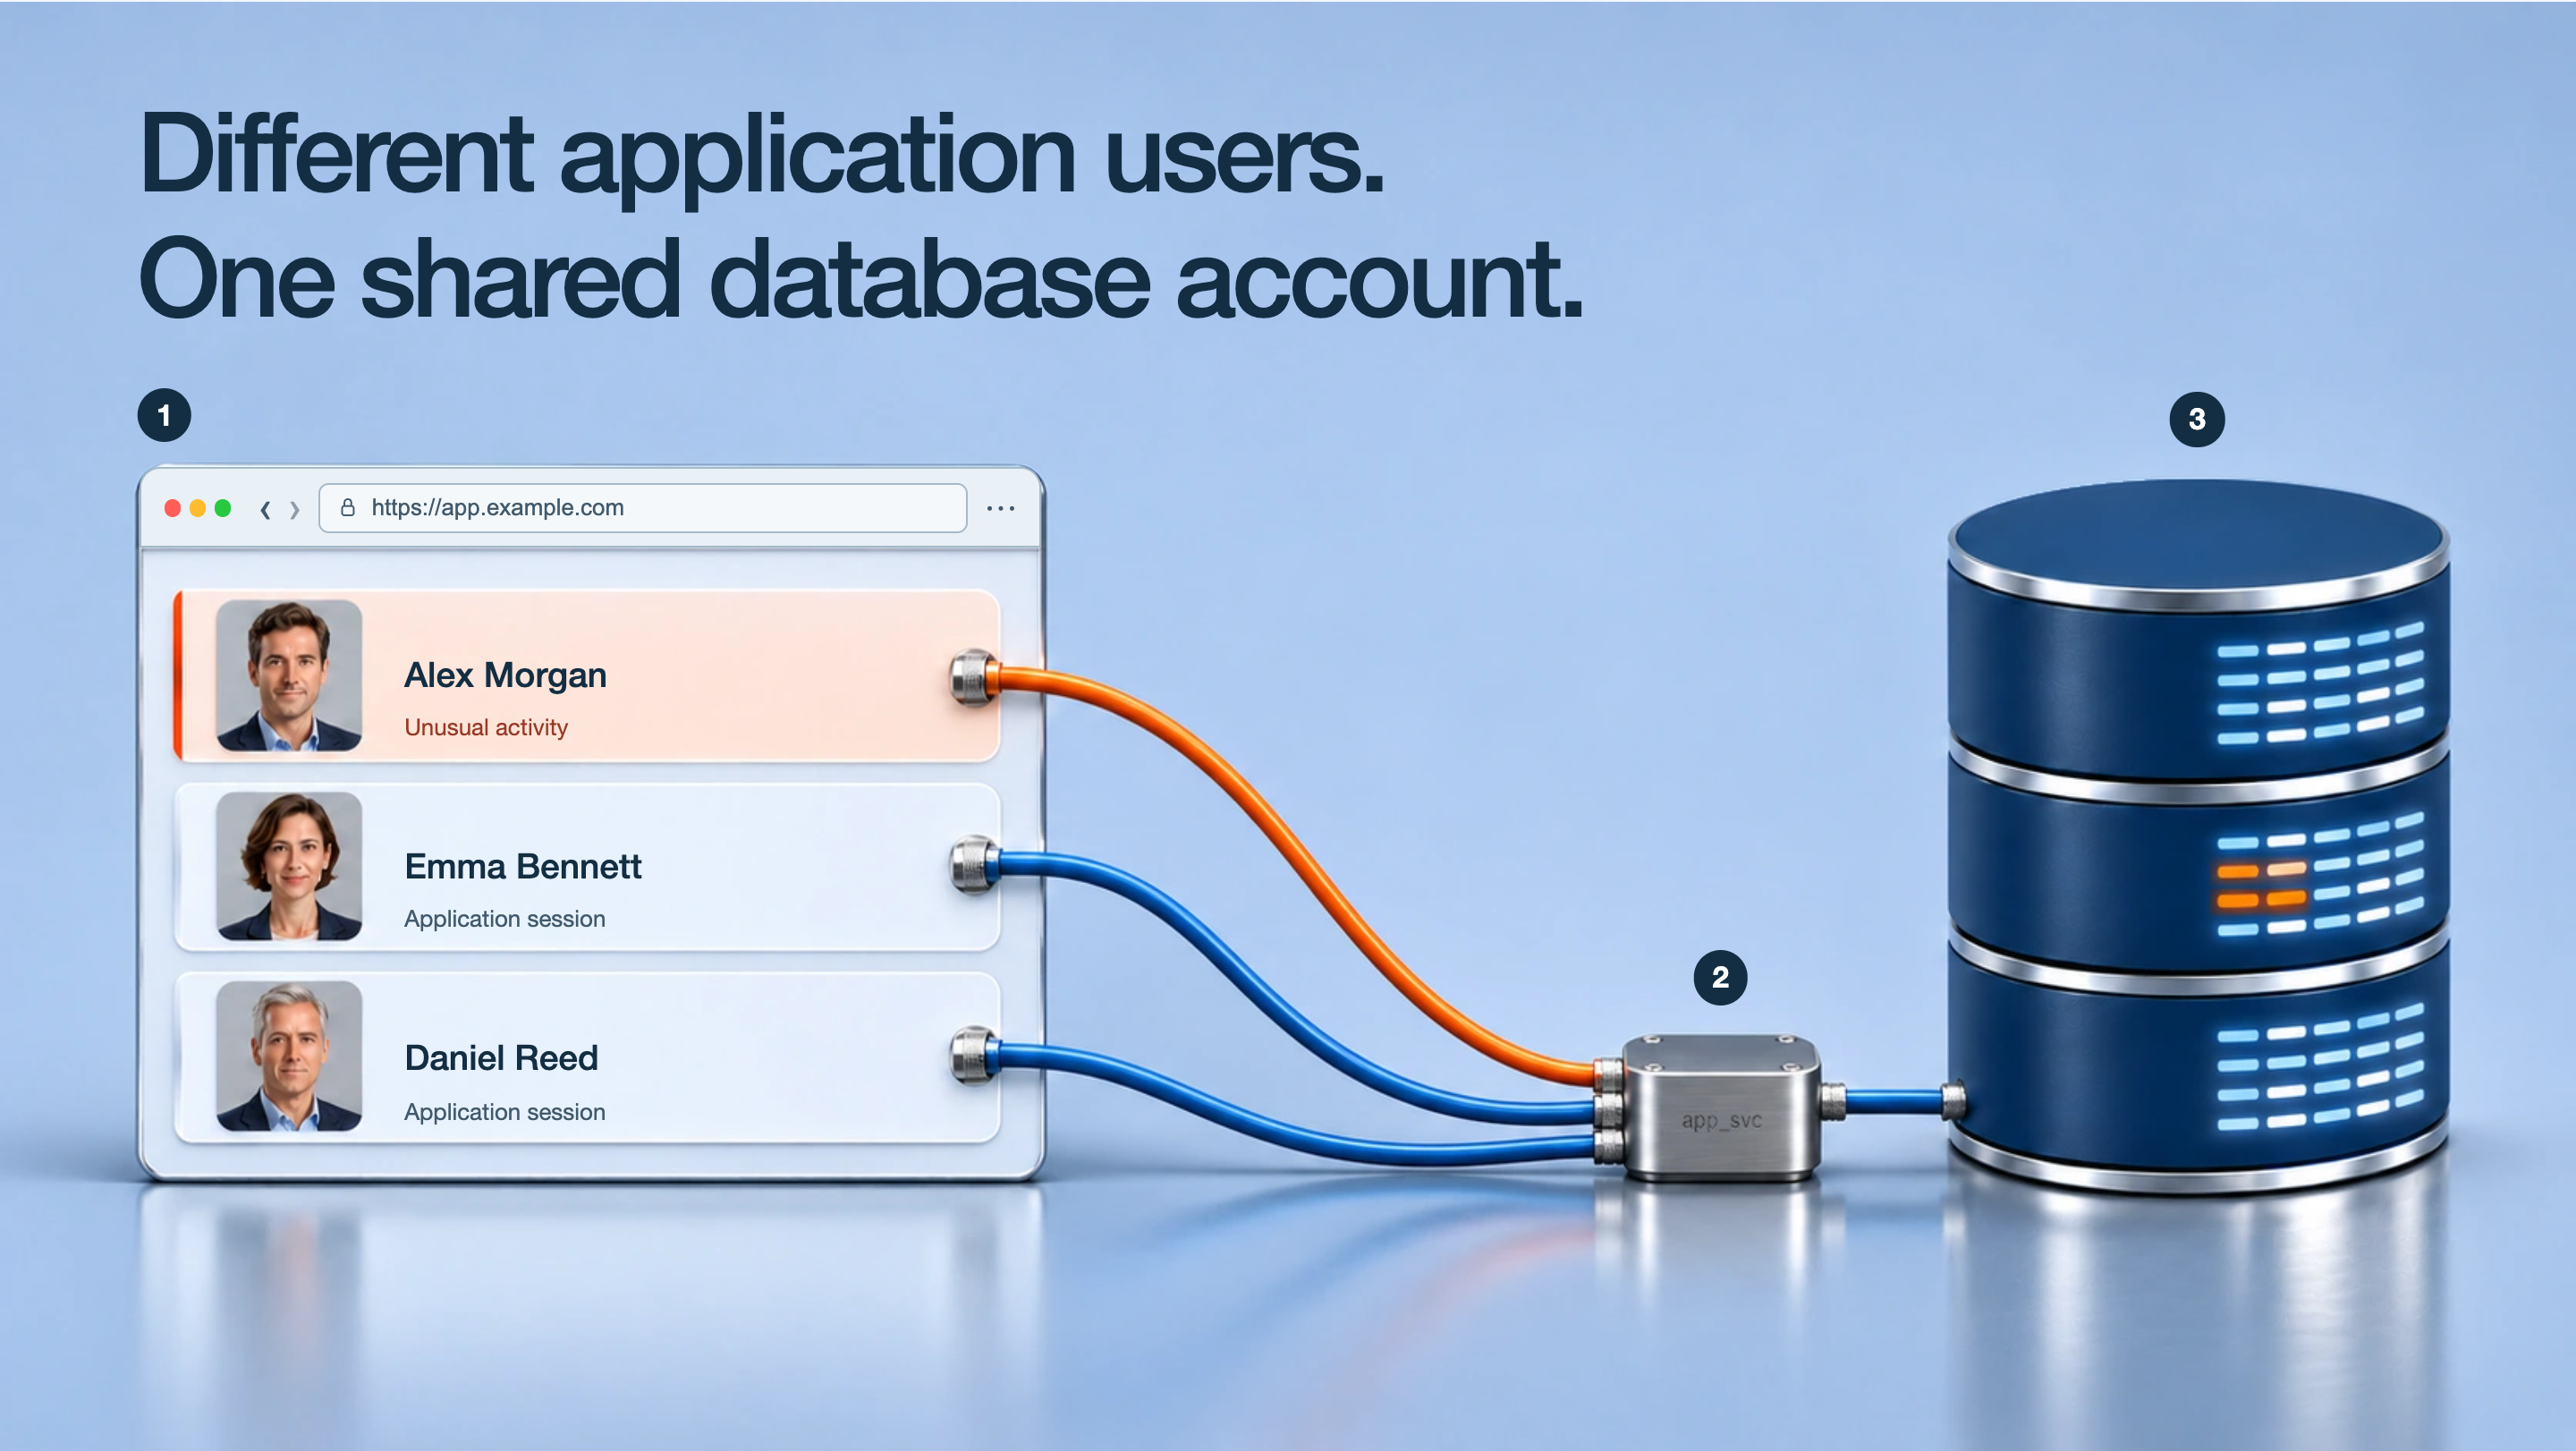
Trace adds available application-user context to SQL statements so compatible monitoring tools can relate database activity to the application request.
Use Trace with Nanori Lens and Oversight, or independently with another compatible monitoring product. Trace does not require a separate connection to Lens.
Integration families are available for Java, Node.js, Python, and .NET. The appropriate method depends on the runtime, framework, driver, and available identity source.
Nanori Trace is optional within Nanori and is also available independently for compatible monitoring products.
Attribution reflects the identity context provided by the application. Missing context remains unknown; a declared identity is not independent proof of who performed an action.
Read the solution brief ↗